
Plexlane · Managed Services
A business can outgrow its managed services long before it outgrows its technology. The warning signs appear between teams: recurring disruption, applications without an owner, recovery plans nobody has tested, and priorities that never reach delivery.
These ten signs apply across IT infrastructure, business applications, cybersecurity, compliance, continuity and technology leadership. Use them to evaluate the complete service model, whether responsibilities sit with an internal team, a managed service provider, specialist partners or a combination.
What does it mean to outgrow managed services?
Your service model no longer reliably supports the business workflows, risks and priorities it is meant to cover—even if individual systems are online and response-time reports look healthy.
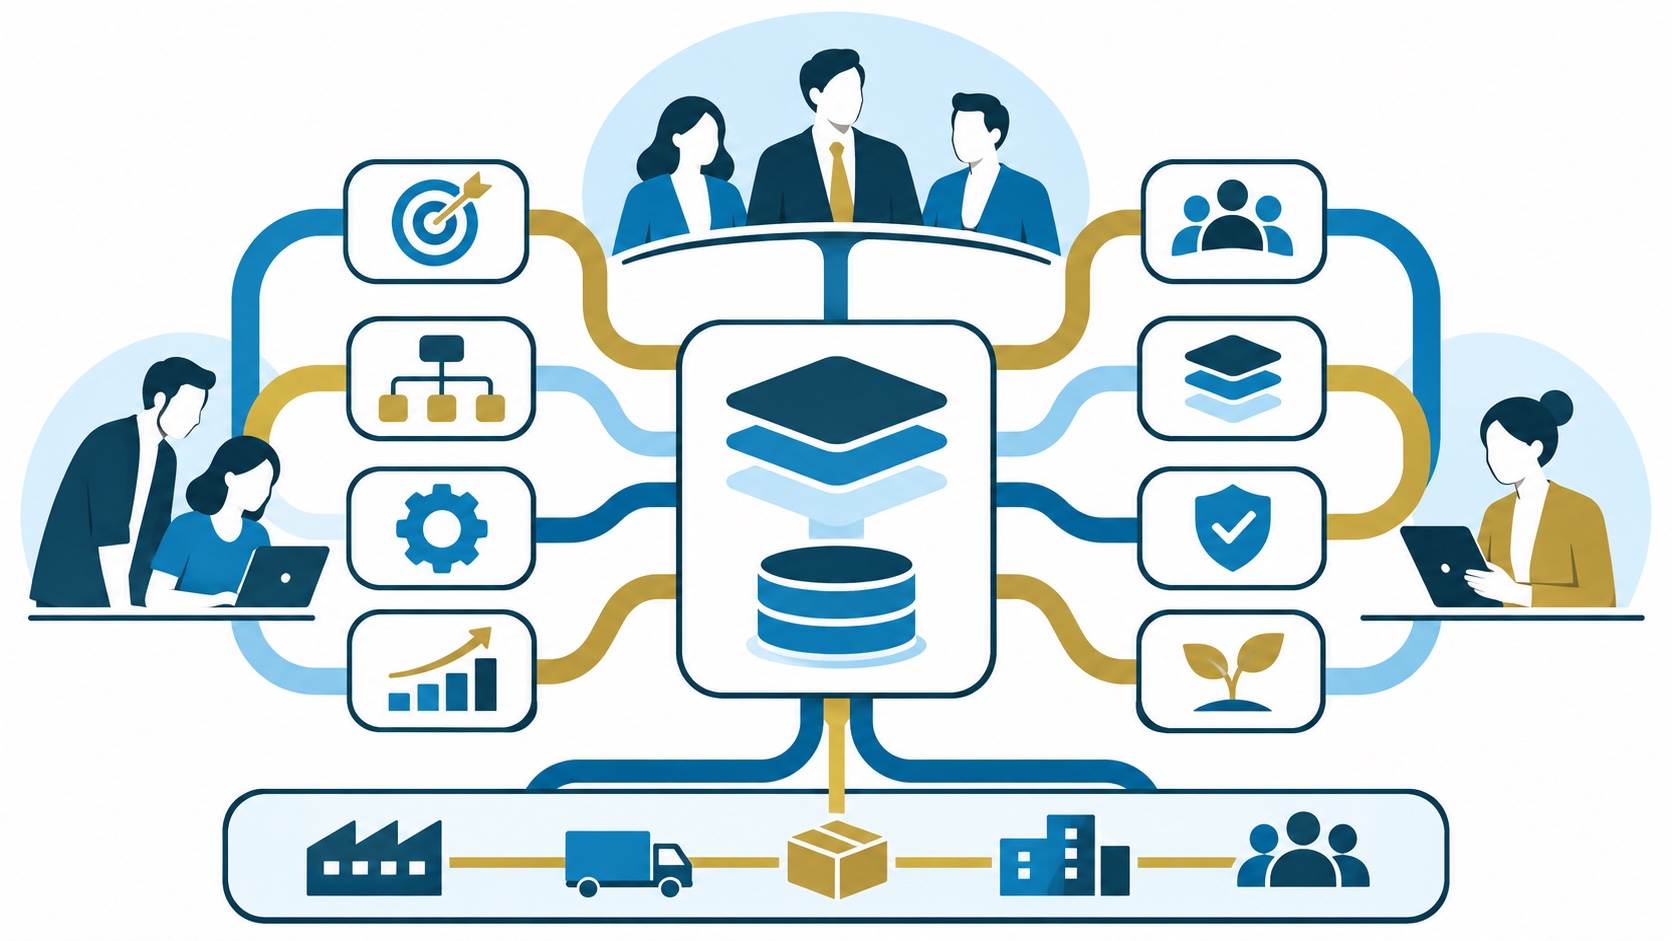
The review in three questions
Does work get done?
Look beyond ticket closure to complete business workflows.
Who owns the gaps?
Make application, security and recovery responsibilities explicit.
Can support grow with you?
Connect capacity and technology decisions to business plans.
Explore this article
01 / Service delivery and application ownership
01The same problems keep returning
Closing a support ticket should mean the underlying problem has been fixed—not simply that a temporary workaround has restored service. Repeated incidents suggest the underlying cause has not been addressed or the permanent fix has no owner.
In practice · ManufacturingA production planner’s ERP scheduling job fails repeatedly. Support restarts it each morning, but nobody investigates the integration error behind the failure. Production continues to depend on a workaround.
Effective support should include a process for investigating recurring problems. Ask which issues repeat, why they recur, and who is accountable for eliminating them.
02Ticket reports look healthy while employees struggle
Fast acknowledgment and closed-ticket counts offer limited insight into whether people can finish their work. A ticket can close while the employee still relies on a spreadsheet or a colleague’s account.
In practice · FinanceAccounts payable reports that invoice imports regularly fail. Each request closes after a manual upload, while the finance team spends extra time checking duplicates and correcting entries.
Review service performance alongside business impact: repeated disruption, complete resolution and user experience. Agree what must be restored or corrected before a ticket is considered finished.
03Critical applications sit outside your support coverage
Your provider handles laptops, email, and connectivity, but the systems running purchasing, inventory, billing, or service delivery fall between contracts. Internal IT, the software vendor, and an implementation partner each cover only part of the problem.
In practice · DistributionOrders stop flowing from an online storefront into the ERP. The storefront provider confirms its service is working; the ERP vendor says the application is available. Nobody owns the connection between them.
Evaluate coverage against complete business workflows. Document who owns application support, integrations, escalation, and coordination when several providers are involved.
02 / Operational control, security and resilience
04Hiring and departures require constant chasing
Growth exposes weaknesses in account administration. New employees wait for equipment and permissions, while departing staff leave behind accounts that nobody has checked.
In practice · Professional servicesA project manager joins with a laptop ready but cannot access client folders or the resource-planning application. Several colleagues interrupt their work to arrange permissions individually.
Repeatable onboarding and offboarding need agreed triggers, role-based access decisions, and completion checks. A reliable process connects HR, managers, and IT through a documented process rather than relying on someone remembering every application.
05A new location creates a new set of standards
An acquisition or branch opening should not leave the company with permanent uncertainty about devices, licenses, networks, and support responsibilities. Local differences may be necessary, but they should be deliberate.
In practice · Healthcare administrationA growing clinic group discovers that each location uses a different process for device updates and remote access. Central support cannot confidently identify which systems are covered or who approves changes.
Ask whether your support model can maintain a reliable inventory, common security practices, and clear site responsibilities while accommodating legitimate operational differences. Expansion should have a repeatable integration plan.
06Backups exist but recovery is an unanswered question
A successful backup notification does not establish how quickly the business can resume operations. Recovery depends on usable data, application dependencies, access, and people who know the procedure.
In practice · Legal operationsA firm backs up matter documents but has never rehearsed restoring permissions and reconnecting the applications that use them. Recovering files alone may not restore the working environment.
The UK National Cyber Security Centre’s technical recovery preparation guidance recommends tested backups, restoration exercises and documented dependencies. Ask your provider to show recovery results for critical business services, including applications, access and configuration—not only successful backup jobs.
07Nobody can explain who owns security decisions
Your organization may have security products without clear accountability for the risks they are supposed to manage. Who accepts an unresolved vulnerability? Who approves remote access exceptions? Who directs the response when an incident affects operations?
The NIST Cybersecurity Framework 2.0 Small Business Quick-Start Guide organizes cybersecurity outcomes into Govern, Identify, Protect, Detect, Respond and Recover. Its governance guidance includes identifying responsibility for developing and executing the security strategy.
Ask for named decision-makers and escalation paths. Technical support, security operations, and executive risk decisions need coordination, even when different people provide them.
| A limited service view | A business workflow view |
|---|---|
| The ERP is online. | Orders reach inventory, fulfillment and billing correctly. |
| Backup jobs succeeded. | Critical applications, permissions and data can be restored together. |
| A security tool is licensed. | Controls are configured, operating and assigned to accountable people. |
03 / Investment, capacity and leadership
08Technology spending is rising without an agreed plan
Emergency replacements, overlapping subscriptions, unused licenses, and separate departmental purchases can obscure what the company is actually paying for. The monthly invoice may explain charges without explaining priorities.
Which systems need replacement? Which subscriptions duplicate capabilities? What investment would remove a recurring operational constraint?
Useful service reporting should make those choices easier to evaluate. Request a current cost baseline and a prioritized roadmap, including dependencies, expected benefits, and the consequences of postponing work.
09Strategic projects never escape the support queue
Your internal team may spend so much time handling urgent requests that application upgrades, automation, and integration work repeatedly slip. Adding projects to the same queue does not create the capacity to deliver them.
Check whether project work has an accountable sponsor, defined scope, protected resources, and a realistic delivery schedule. Distinguish ongoing service responsibilities from implementation commitments so neither disappears behind the other.
An appropriate service model can combine operational coverage with specialist project capacity. Senior technology leadership can help sequence investments and resolve decisions that a help desk should not have to make.
10Business plans and service planning stay disconnected
Leadership discusses acquisitions, new services, customer requirements, or AI adoption, but IT learns about them after commitments have been made. Support is then expected to deliver quickly within constraints it had no opportunity to assess.
Bring technology planning into business planning early. Review the implications for applications, data, access, security, staffing, and ongoing service costs before approving a major change.
A support arrangement suited to growth should include regular planning conversations. It should help leadership understand which ambitions current systems can support and where preparation is needed.
What to review before changing your managed services
Build an evidence base
Review tickets, outages, invoices, and employee feedback for patterns across departments.
- Which recurring issues interrupt revenue, production, or client delivery?
- Which applications and integrations lack clear support ownership?
- Where do internal teams depend on undocumented workarounds?
- What evidence demonstrates recovery and security readiness?
- Which business priorities lack a funded technology plan?
Match the service to the gap
You may need broader application coverage, clearer provider responsibilities, extra delivery capacity or fractional CIO or CISO leadership. Compare proposals against the gaps you can demonstrate. Each proposal should explain ownership, escalation, exclusions, transition arrangements and how performance will be reviewed.
Give your next stage of growth the right support
When recurring disruption and stalled priorities become normal, reassess the managed services behind them. Plexlane connects infrastructure and IT operations, business application support, cybersecurity and technology leadership. Explore our enterprise managed services or discuss the gaps in your current service model.
Managed services: frequently asked questions
Does outgrowing support mean replacing our internal team?
No. Additional expertise or service capacity can support an internal team. Define the gaps and decide which responsibilities belong internally, externally, or with a shared team.
How should we compare managed service providers?
Compare application coverage, escalation ownership, security responsibilities, recovery testing, and planning support. Review exclusions and how the provider measures complete resolution, alongside price and response commitments.
Is slow response the strongest warning sign?
It is one signal. Repeated failures, unclear ownership, and unresolved business disruption can matter just as much, even when the first response arrives quickly.
When does part-time CIO or CISO leadership help?
It can help when the business needs senior guidance on investment, architecture, security priorities, or governance without requiring a full-time leadership role.
What should happen before a provider transition?
Confirm administrative access, documentation, licenses, backups, open issues, and contractual obligations. Agree on a transition owner and handover plan that protects ongoing operations.
Connect the gaps to a practical service plan
Bring your recurring issues, application dependencies and growth priorities. Start with what the business needs to accomplish.