
Plexlane · CMMC & Compliance
The suspension of CMMC Phase II changes an implementation milestone; it does not resolve weaknesses in your environment. For defense suppliers, this is a practical time to examine where sensitive information travels, whether security controls work, and what leadership can support with evidence.
A useful readiness assessment gives your business a defensible starting point: an agreed scope, demonstrated controls, and a prioritized plan for the gaps. Start with the workflows and responsibilities behind those findings before committing to more tools.
What is a CMMC readiness assessment?
An advisory review of your assessment scope, implemented controls and supporting evidence. It identifies preparation gaps and remediation needs; it does not confer CMMC status or replace a required formal assessment.
Readiness at a glance
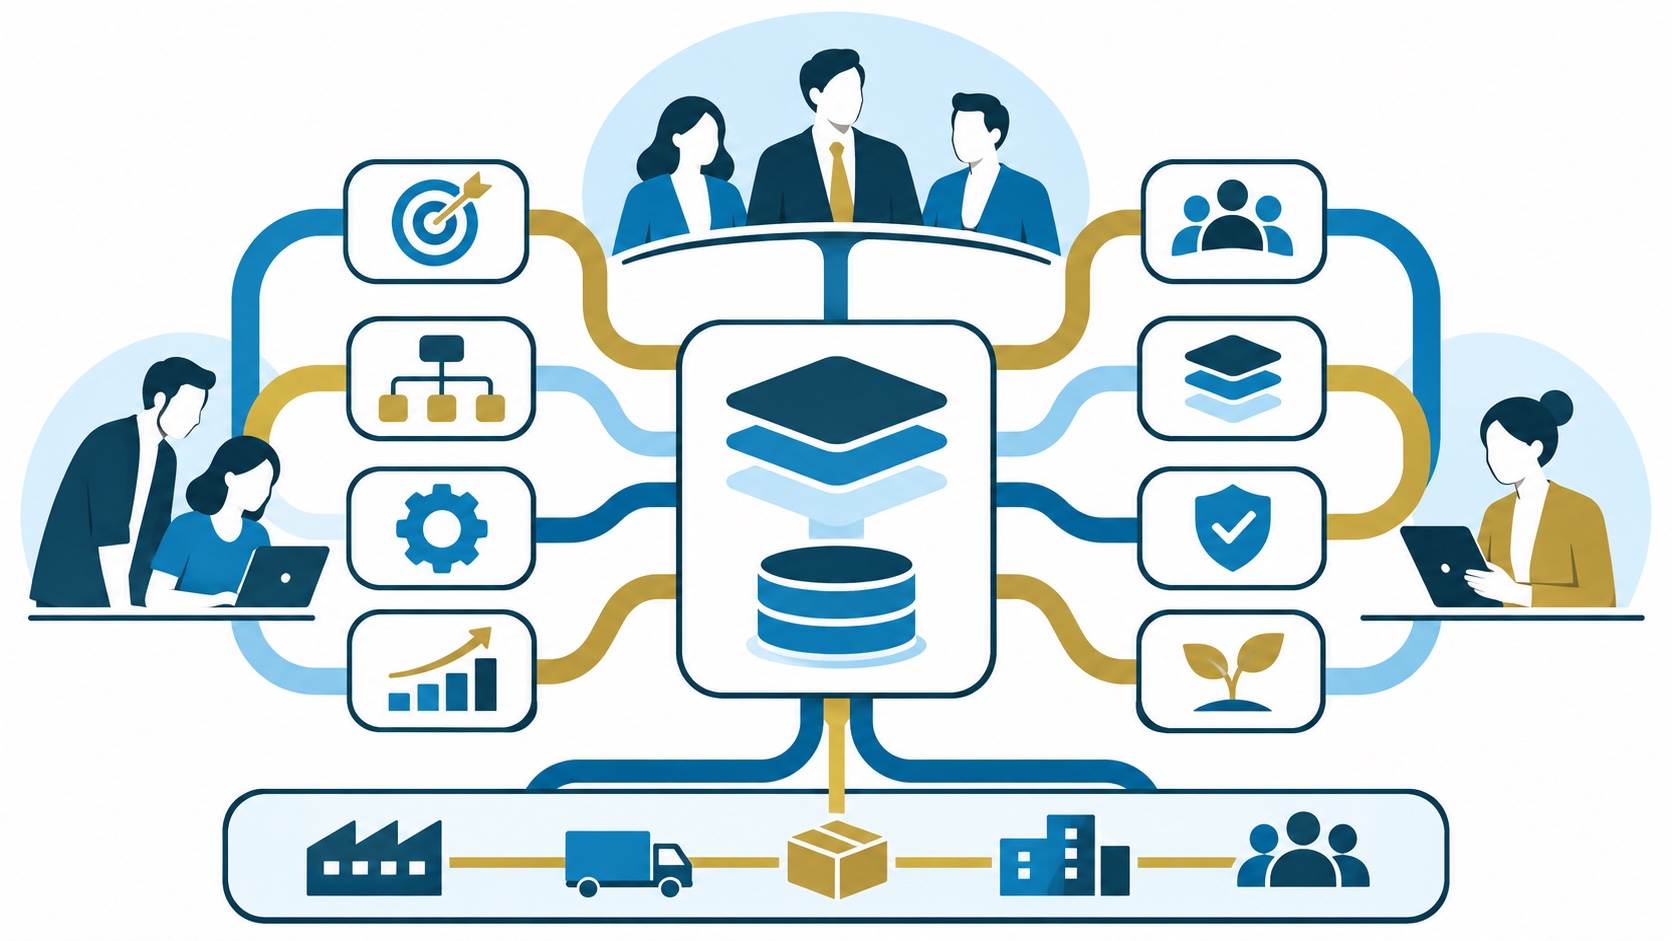
Scope the information
Follow CUI through the people, systems and providers that handle it.
Test the evidence
Check what controls actually do in everyday business events.
Fund the next steps
Give each gap an owner, resources and a way to verify closure.
Explore this article
What the Phase II suspension changes
On July 13, 2026, the Department announced the suspension of CMMC Phase II requirements, previously scheduled for November 10, 2026. The official announcement states that Phase I self-assessment requirements remain in place. Treat the change as a timeline update, not a blanket waiver of cybersecurity responsibilities.
Where applicable, DFARS 252.204-7012 still requires safeguarding covered defense information and reporting qualifying cyber incidents. Your contracts, solicitations and subcontract terms remain the starting point for deciding what your company must do.
Avoid treating an industry headline as permission to change your compliance position. Have contracts and security leaders review your actual obligations together, including applicable self-assessments, Supplier Performance Risk System submissions, and affirmations. Monitor official updates rather than assuming when third-party requirements will return.
What a CMMC readiness assessment should reveal
A CMMC readiness assessment is an advisory preparation exercise: it compares your environment, practices and evidence with applicable requirements. It does not confer CMMC status or replace a required formal assessment.
The useful output is more than a score. Leadership needs to know which systems are in scope, which requirements are implemented, which claims lack evidence, and what remediation will cost. Each finding should have an owner, a target date, and a clear method for verifying closure.
Start with information flows before buying tools
Engineering and aerospace suppliers
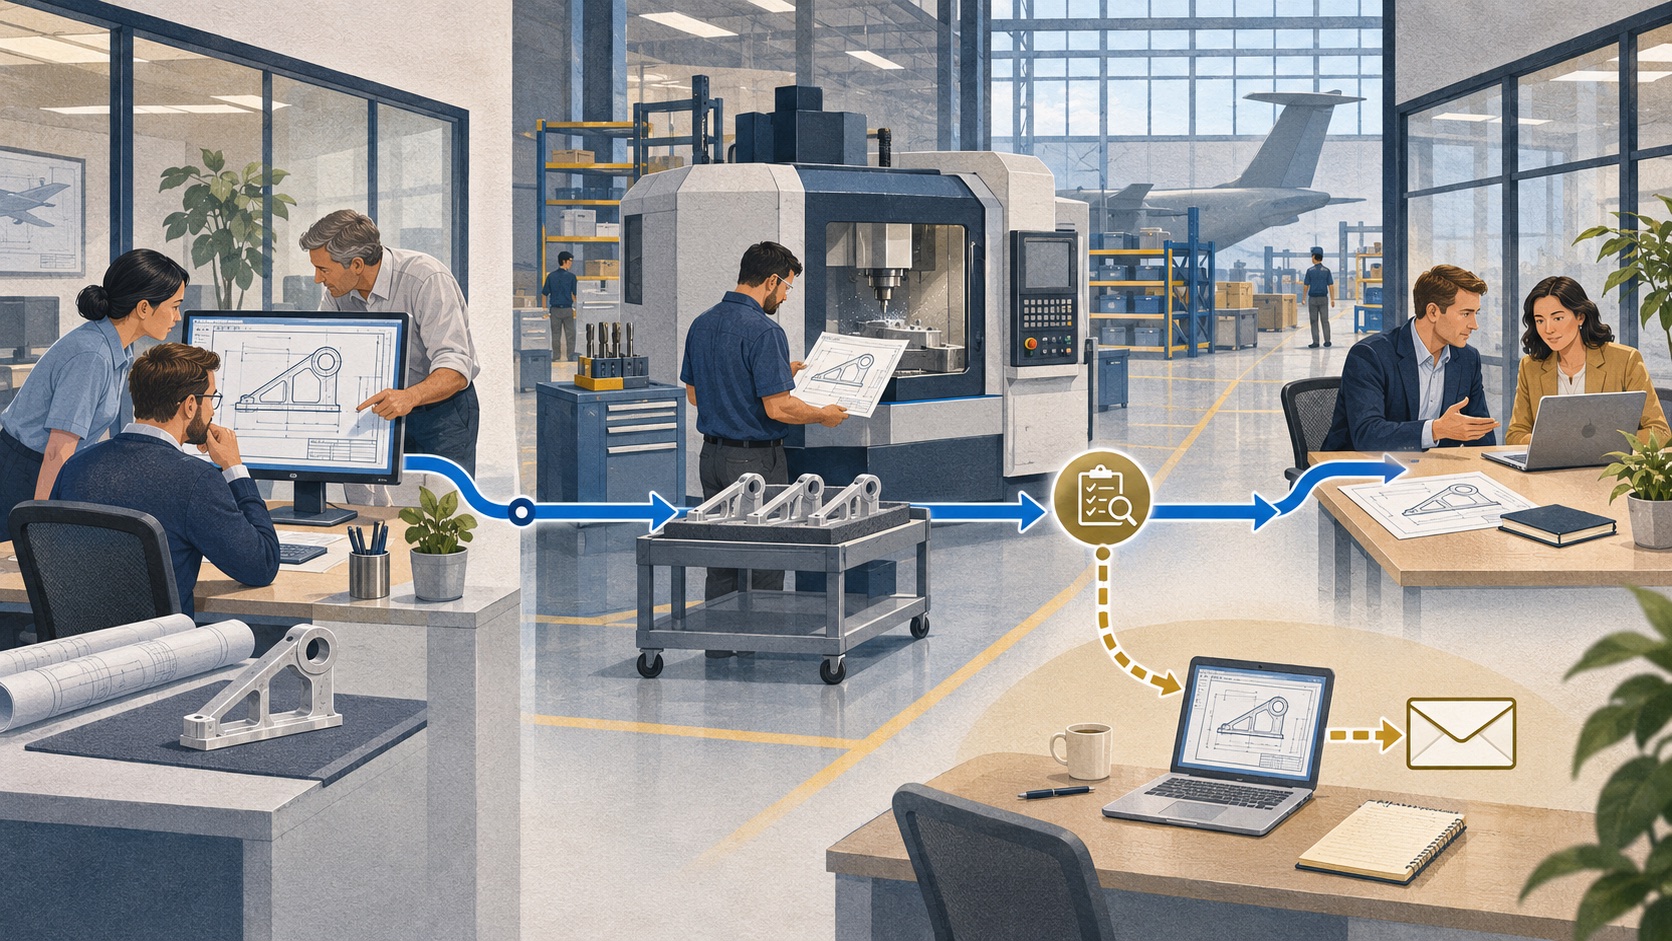
Illustrative scenarioConsider an aerospace component supplier whose engineers use an approved repository for controlled drawings. To resolve an urgent production issue, someone exports a drawing to a laptop and emails it to a subcontractor. The central repository may be protected, but the information has moved beyond the assumed boundary.
Trace how controlled unclassified information (CUI) is received, created, stored, transmitted and disposed of. Include email, collaboration platforms, endpoints, backups, removable media and paper records where relevant to the scope. Establish which information requires protection before drawing the system boundary.
Start with a real workflow: follow a drawing from receipt through engineering review, production, and supplier coordination. Interview the people doing the work. Their shortcuts often reveal dependencies that a network diagram misses.
Manufacturing and the shop floor
Illustrative scenarioA precision manufacturer may have a production workstation connected to equipment that cannot easily be upgraded. Operators share an account because individual sign-ins appear to slow production. Office controls look mature, while the shop floor has different access and maintenance practices.
Document those constraints before selecting a fix. Evaluate the workstation’s role, its exposure to CUI, and the applicable requirements. Segmentation, access changes, or replacement may be appropriate, but a business justification alone does not make a deficiency compliant.
Test controls through everyday business events
HR and employee departures
Illustrative scenarioAn electronics supplier removes a departing employee from payroll promptly, but nobody tells the administrator responsible for a separate engineering application. The employee’s main account is disabled while another access route remains available.
Use the review to walk through a recent departure. Check approvals, account inventories, revocation records, and device returns. Compare the written offboarding procedure with what happened in each system.
This exercise also identifies ownership gaps. HR can trigger the process, managers can confirm required access changes, and IT can execute them. Someone must verify that the entire process finished.
Software development and remote access
Illustrative scenarioA defense software subcontractor enables multifactor authentication for employee email but overlooks a separate remote administration service. Its security presentation says MFA is enabled, yet the statement covers only part of the environment.
Review authentication by access path and account type. Examine privileged access, remote sessions, service accounts, and exceptions against the applicable requirements. Test configurations directly rather than relying on a product license or a dashboard summary.
The review should distinguish between a capability you purchased, a control you configured, and a control you can demonstrate operating as required.
Examine suppliers and rehearse incident reporting
Procurement and external service providers
Illustrative scenarioA maritime equipment supplier contracts with a cloud backup provider. Procurement evaluates price and recovery speed, while security assumes the provider’s general compliance statement covers defense information. Neither team has verified the actual service configuration or contractual responsibilities.
For external cloud services that store, process or transmit covered defense information in contract performance, DFARS 252.204-7012 requires security equivalent to the FedRAMP Moderate baseline and the relevant incident, preservation and investigation obligations. Review the specific service and configuration, the provider evidence and the contract responsibilities. A broad marketing claim is insufficient.
Build a responsibility matrix for internal teams, managed service providers, cloud providers, and subcontractors. Identify who implements each control, supplies evidence, responds to incidents, and approves changes.
Operations and incident response
Illustrative scenarioImagine a logistics subcontractor discovering suspicious activity late on Friday. The IT provider begins investigating, but operations waits until Monday to notify the person responsible for contractual reporting. The technical response has started; the reporting process has stalled.
For incidents within the clause’s reporting provisions, DFARS 252.204-7012 defines rapid reporting as within 72 hours of discovery. Rehearse who evaluates reportability, who submits the report and how relevant evidence is preserved. The same clause requires preserving affected-system images and relevant monitoring or packet-capture data for at least 90 days after submission of the incident report.
Run the exercise outside normal working hours on paper. If a key decision depends on one unavailable person, revise the escalation process before a real incident exposes the problem.
Turn findings into a funded remediation plan
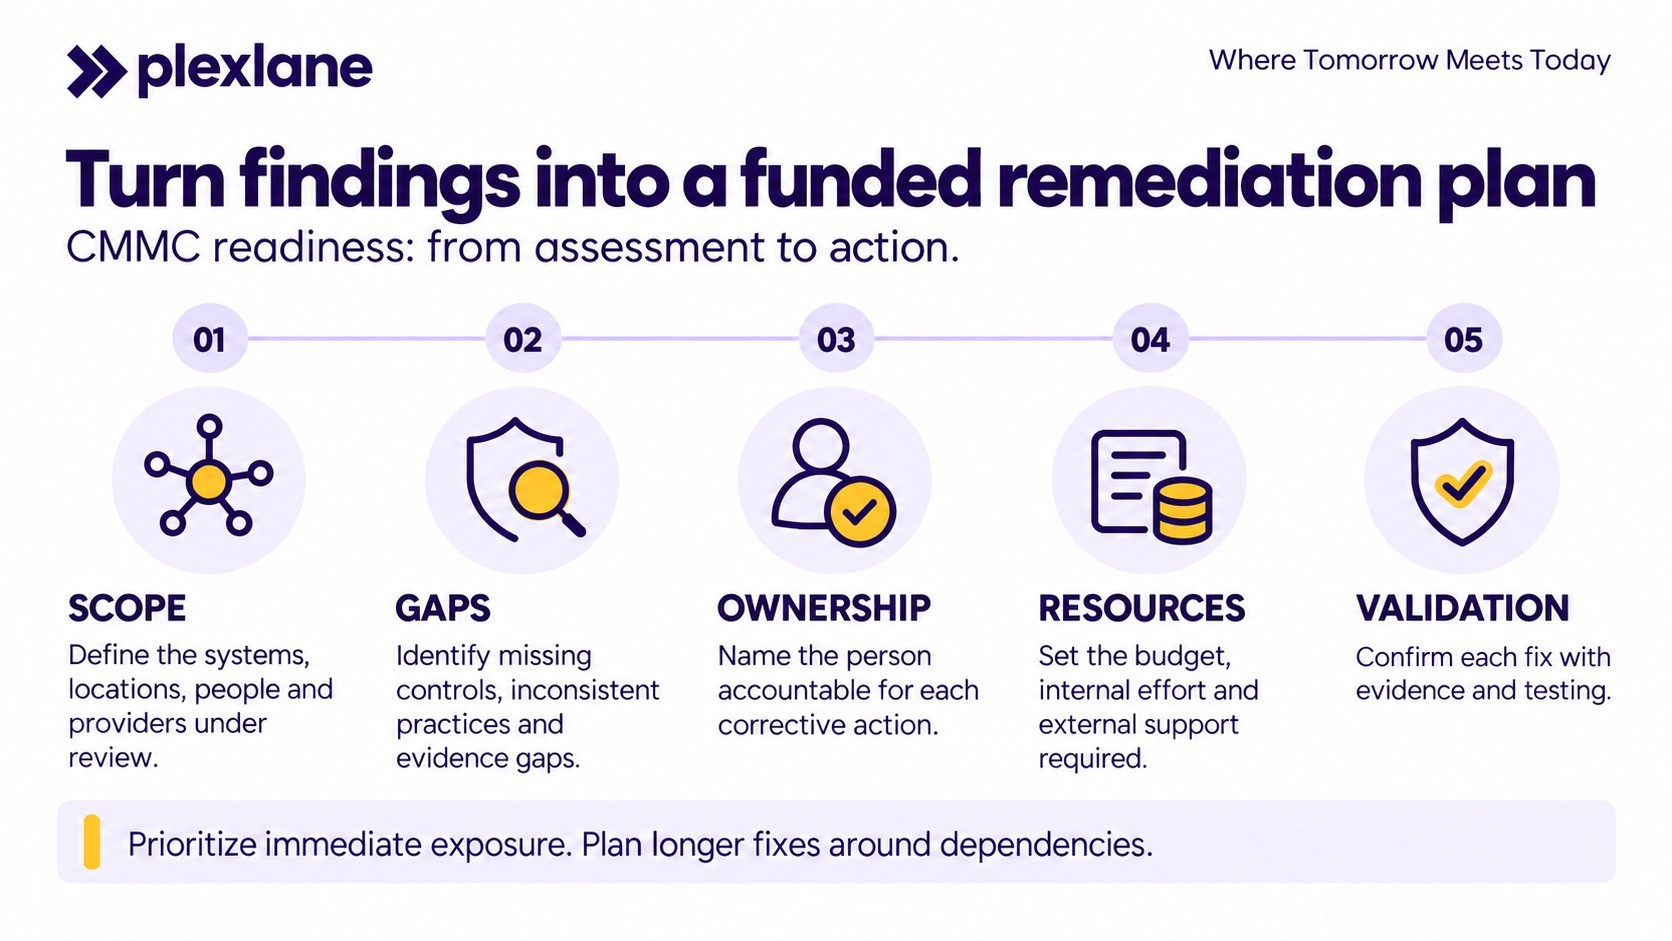
The assessment becomes useful when findings translate into decisions. Separate immediate exposure from longer implementation work, and identify dependencies that could delay progress.
- Scope: Systems, locations, people, and providers included in the review.
- Gaps: Missing controls, inconsistent practices, and insufficient evidence.
- Ownership: A named person accountable for each corrective action.
- Resources: Budget, internal effort, and external support required.
- Validation: Evidence and testing needed to confirm that each fix works.
Keep the system security plan aligned with the actual environment. Use remediation tracking to manage unfinished work, but do not assume a plan of action automatically permits an unmet requirement under every assessment or contract.
Set a recurring review with IT, operations, procurement, and leadership. Measure verified closures and unresolved dependencies rather than reporting progress solely through a rising score.
Build readiness that survives the next timetable change
The strongest outcome is an environment your team understands and can support consistently. That takes time: employees must adopt revised processes, providers must resolve responsibility gaps, and evidence must reflect operations after changes are implemented.
Plexlane can help defense suppliers connect security readiness with the people, systems and decisions needed to act on findings. Explore our cybersecurity, CMMC and compliance services or start a readiness conversation to discuss your scope and priorities.
CMMC readiness: frequently asked questions
Is CMMC canceled because Phase II is paused?
No. The July 13, 2026 announcement suspends Phase II implementation and states that Phase I self-assessment requirements remain in place. Check current official guidance and your contract requirements before changing your compliance plans.
Does a CMMC readiness assessment provide certification?
No. It identifies preparation gaps and remediation needs. Formal CMMC status requires the applicable assessment and submission process; an advisory review cannot replace it.
Which departments should participate?
Include IT, security, engineering, operations, HR, procurement, and contracts personnel where their work affects the assessment scope. Involve relevant external providers and an executive sponsor who can approve resources.
Should we stop security investments until the timeline changes?
Continue work needed to meet existing obligations and address known exposure. For larger purchases, confirm scope, applicable requirements, and implementation dependencies before committing funds.
How often should readiness be reviewed?
Refresh the review after material changes to systems, providers, locations, or CUI workflows. Revisit open findings regularly, and separately track the formal assessment and affirmation schedules applicable to your contracts.
Make readiness actionable
Connect your CMMC readiness findings to a clear scope, accountable owners and a practical remediation plan. Explore Plexlane’s cybersecurity, CMMC and compliance services.